

UK law does not impose blanket data residency on cloud services. There is no statute forcing every business to keep data on British soil. Residency becomes mandatory only in specific cases: public-sector contracts, regulated sectors like health and finance, and situations involving special-category personal data. For everyone else, the Data Protection Act 2018 and ICO guidance care far more about your contractual safeguards than your postcode. Check vendor regions, sub-processor lists, and transfer clauses before you assume residency is even the right question.
TL;DR:
- UK law mainly requires data residency in specific regulated sectors and when handling sensitive personal data, but not for all businesses or general use cases.
- Data sovereignty refers to which country's laws govern the data, independent of its physical location, making jurisdiction checks vital beyond just hosting regions.
- Verifying a vendor’s UK residency involves checking exact storage, processing locations, sub-processor lists, support access points, and contractual commitments on data flow and government requests.
- Cross-border data transfer risks are reduced when UK-recognized adequacy applies; otherwise, detailed transfer risk assessments and contractual safeguards are necessary.
- AI deployments should specify where model inference happens and include documented sub-processor details, as AI model calls can cross borders invisibly and impact residency compliance.
Table of Contents
- What is data residency, and how does it differ from data sovereignty?
- What UK laws and government guidance govern cloud data location?
- When does UK data residency genuinely matter for your organisation?
- How do you verify a vendor's UK residency claim is credible?
- How do you assess and mitigate cross-border transfer risk?
- Which procurement questions should you ask cloud and AI vendors?
- How does Gmdautomation approach UK residency in managed AI deployments?
- What the residency conversation gets wrong
- Get UK-compliant AI automation without the compliance guesswork
- Where to check the official rules yourself
- Sources
- FAQ
What is data residency, and how does it differ from data sovereignty?
Data residency refers to the physical location where your data sits and gets processed, the actual server rack in an actual building. Data sovereignty is a different animal entirely: it concerns which country's laws govern that data and the company holding it, regardless of where the servers physically live.
This distinction trips up more IT teams than it should. A cloud provider can store your data in a London data centre and still be subject to foreign legal demands if its parent company is headquartered abroad. The US CLOUD Act is the clearest illustration: American law enforcement can compel a US company to hand over data it controls, even when that data physically sits in a UK server room.
Practical gaps worth checking before you sign anything:
- Storage location versus processing location, since backups and analytics often run somewhere different from primary storage
- The provider's legal entity and parent company jurisdiction, not just the marketing page's claimed hosting region
- Metadata and telemetry, which frequently gets processed in a different location from the data it describes
- Support access, because staff resolving your ticket might be logging in from outside the UK entirely
Residency answers "where." Sovereignty answers "under whose authority." You need both answers, not just one.
What UK laws and government guidance govern cloud data location?
UK GDPR and the Data Protection Act 2018 set the rules for international transfers and processing, requiring organisations to apply transfer safeguards whenever data moves, or becomes accessible, outside the UK. The Data Protection Act 2018 remains the backbone here, and it doesn't ban overseas processing outright. It demands evidence that appropriate protections exist.
The Data Use and Access Act 2025 has since updated some of the mechanics around cross-border data access and transfer procedures for certain data categories. If your organisation handles anything unusual (health records, biometric data, law enforcement data), it's worth reading the Gov directly rather than relying on second-hand summaries.
On the practical side, GOV.UK's guidance is refreshingly blunt: overseas hosting is permitted for OFFICIAL data when legal, data protection, and security arrangements are satisfactory. The public sector's Cloud First policy actively encourages considered use of overseas regions where resilience or capability genuinely benefit from it.
Key threads to pull together:
- UK GDPR and the Data Protection Act 2018 govern lawful transfer mechanisms
- The Data Use and Access Act 2025 adjusts access procedures for select data categories
- Gov treats residency as a risk decision, not a default requirement
- ICO guidance on adequacy decisions shapes when a transfer risk assessment is even necessary
When does UK data residency genuinely matter for your organisation?
Residency stops being theoretical the moment you're bidding for certain contracts or handling certain data. Here's when it becomes a real requirement rather than a nice-to-have:
- Regulated sectors. NHS bodies, FCA-regulated financial firms, defence contractors, and critical national infrastructure operators routinely face explicit residency expectations baked into sector regulation or client mandates.
- Public-sector procurement. Framework agreements and government contracts frequently include residency clauses as a condition of bidding, not a preference.
- Special-category personal data. Health records, biometric data, and similarly sensitive categories raise the stakes on where processing happens and who can access it.
- Client-imposed contract terms. Even outside regulated sectors, a major client may simply insist on UK-only processing as a term of doing business with them.
For most standard SaaS use cases, residency is less critical than getting the basics right: solid processing terms, sub-processor visibility, and a proper transfer risk assessment. Chasing UK-only hosting when your risk profile doesn't demand it usually means paying a repatriation premium for protection you didn't need. Map your data sensitivity against actual regulatory or contractual obligations first, then decide your residency posture. Don't do it the other way round.
How do you verify a vendor's UK residency claim is credible?
Marketing copy that says "hosted in the UK" is not evidence. A genuine residency commitment covers storage, processing, backups, and support access, and you should be able to see documentation for all four.
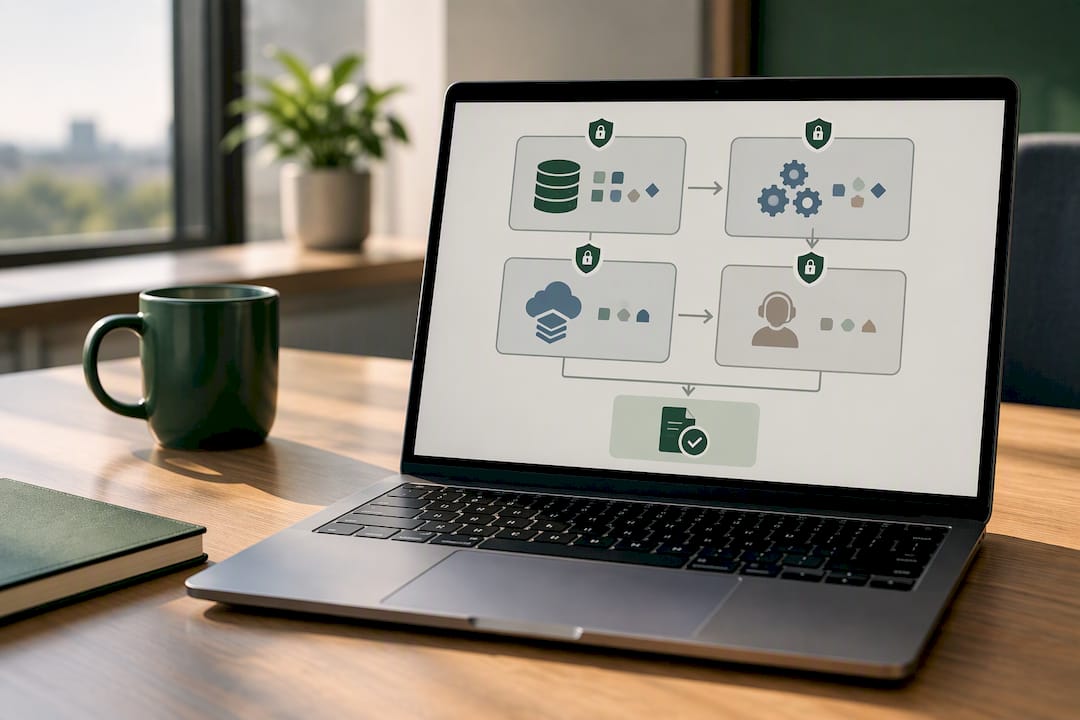
Start with the basics: ask for named UK data-centre locations, not vague regional descriptions. Demand confirmation of where primary processing happens, where backups live, and where disaster-recovery failover points are, because a vendor can be entirely honest about UK primary storage while its DR site sits in another country.
Sub-processors deserve equal scrutiny. Request a current, dated sub-processor list and, ideally, contractual rights to object if the vendor adds an off-UK sub-processor later. Support operations matter just as much: follow-the-sun support models frequently give non-UK staff access to your systems and data, even when storage itself never leaves British soil.
A few more checks that separate real residency guarantees from marketing gloss:
- Confirm whether telemetry, logs, and metadata are covered by the same residency commitment as your primary data, not treated as an exception
- Ask about encryption at rest and in transit, and whether customer-managed keys (CMKs) are available so you retain control independent of the provider
- Request architecture diagrams showing data-flow boundaries, plus a written policy on how the vendor handles foreign government access requests
- Check whether the vendor can produce audit logs on demand rather than promising them in principle
Pro Tip: Ask for the sub-processor list and the foreign-access policy in the same email. Vendors happy to talk about UK hosting often go quiet when asked who else touches the data and under what legal compulsion.
How do you assess and mitigate cross-border transfer risk?
Adequacy decisions simplify things considerably: where the UK has recognised a country's data protection regime as adequate, transfers there don't require the extra paperwork of a full transfer risk assessment. Outside adequacy, a Transfer Risk Assessment (TRA) becomes necessary, and UK guidance expects one whenever data moves to a jurisdiction without that recognition, or whenever a vendor's sub-processor chain introduces a country you haven't assessed.
A TRA isn't a box-ticking exercise. It should genuinely weigh the destination country's surveillance laws, the sensitivity of the data involved, and whether contractual safeguards can realistically offset legal gaps.
Mitigations that actually reduce exposure, rather than just looking good in a policy document:
- Standard contractual clauses combined with explicit residency and breach-notification terms
- Audit rights written into the contract, not offered as a courtesy
- Customer-managed keys (CMKs) so the vendor cannot access readable data without your involvement
- Pseudonymisation before data reaches higher-risk processing stages
- Regionalised processing for AI agent calls, so voice or chat interactions don't silently route through an overseas model endpoint
Sovereign cloud or air-gapped infrastructure is justified only for genuinely high-stakes cases (defence, certain health data). It comes with real trade-offs: higher cost, slower feature releases, and less flexibility than mainstream hyperscale platforms.
Which procurement questions should you ask cloud and AI vendors?
Treat this as your minimum interrogation list before signing anything:
- Which regions host primary processing, backups, and disaster-recovery failover, and are they named specifically?
- Who are the current sub-processors, and what notice period applies before adding new ones?
- Where is privileged support access performed from, and does a follow-the-sun model apply?
- For AI features specifically, where do model calls actually execute, and can an agent's action trigger an off-region data transfer without your knowledge?
- Can the vendor provide customer-managed keys (CMKs) and produce audit logs on request rather than on a sales call?
On the contract side, push for explicit residency guarantees, defined notification periods for any sub-processor change, audit rights, and continuity clauses covering what happens if the vendor needs to substitute infrastructure. For AI-specific tools, our guide to UK AI regulation and our vendor procurement checklist go deeper into wording that actually holds up.
How does Gmdautomation approach UK residency in managed AI deployments?
AI automation systems for voice call handling and social media management can be designed with UK compliance requirements included from the start rather than added later. That means named-region hosting, documented sub-processor transparency, and customer-managed key options sit alongside the operational side of the system, not as an afterthought once something goes wrong.
For IT decision-makers gathering evidence for a DPO or an auditor, having a managed provider that already tracks these details removes a genuine administrative burden. Our guide to managed AI contracts covers how contractual structure reduces this risk further.
What the residency conversation gets wrong
Most residency advice treats "where is my data stored" as the whole question, and it isn't even the hardest part. The Data Protection Act 2018 and ICO guidance care about accountability and safeguards far more than geography. A vendor with impeccable UK data centres and a sloppy sub-processor list has told you nothing useful about your actual exposure.
The bigger failure I see in procurement conversations is treating residency as binary: UK or not UK, tick or cross. It isn't. It's a sliding scale of risk that should map directly to what you're actually processing. A marketing SaaS tool storing email addresses doesn't need the same posture as a system handling NHS patient records, yet plenty of organisations apply identical scrutiny to both, wasting budget on the low-risk case and possibly under-scrutinising the high-risk one.
AI adds a genuinely new wrinkle that older residency frameworks weren't built for: an AI agent can trigger a model call that crosses a border in milliseconds, entirely invisible in a standard architecture diagram. If you're deploying AI automation and haven't asked where the model inference actually runs, you haven't finished the residency conversation. You've barely started it.
— Ravi
Get UK-compliant AI automation without the compliance guesswork
Gmdautomation is the practical route to UK-aware AI deployment when you'd rather not build residency evidence from scratch yourself. Managed AI systems may include documented processing regions, sub-processor transparency, and customer-managed key options as part of the subscription service.
The subscription typically covers implementation, ongoing operation, and audit-trail evidence without upfront capital costs. Our Your AI Answers, Qualifies and Books service starts from £300 per month, while Your AI Credit Controller for Lettings starts from £250 per month, both built with UK GDPR obligations in mind rather than retrofitted after a client asks awkward questions. If you're weighing up a vendor's residency claims against your own procurement checklist, visit our services page and see exactly what a compliant deployment looks like before you commit to anything else.
Where to check the official rules yourself
- Gov sets the public-sector policy position on overseas hosting
- The Data Protection Act 2018 is the primary legal text governing transfers
- ICO guidance explains adequacy decisions and transfer risk assessments in practice
- Gov covers procurement expectations
Sources
- Gov
- Legislation
- Sovereign cloud after London Tech Week: when does UK data residency actually matter? - Northern Star
- Is cloud data sovereignty all just a case of ‘Trust me, bro’? | Computer Weekly
FAQ
Are there any UK-based cloud providers?
Yes, several UK-headquartered cloud and hosting providers offer UK-only data centre regions, alongside the UK regions operated by major international hyperscale platforms. The choice between a UK-based provider and a UK region of a global platform usually comes down to your sub-processor tolerance and support-location requirements, not availability.
Does the UK still fall under GDPR?
Yes, the UK operates its own version known as UK GDPR, which sits alongside the Data Protection Act 2018 following Brexit. It mirrors EU GDPR closely but is enforced domestically by the ICO, with its own adequacy framework for international transfers.
Is cloud computing in demand in the UK?
Demand for cloud services among UK businesses continues to grow, driven partly by AI adoption and partly by the shift away from on-premises infrastructure. That growth is exactly why residency and sub-processor transparency questions have become more pressing for procurement teams rather than a niche legal concern.
What is the difference between data residency and data sovereignty?
Data residency is about where your data physically sits, while data sovereignty concerns which country's laws apply to that data and the company controlling it. A provider can host your data in the UK and still be legally compelled by a foreign government if its parent company falls under that country's jurisdiction.