

IT and security teams evaluate AI vendors to manage three categories of risk simultaneously: operational failure, regulatory exposure, and commercial lock-in. Get any one of those wrong and the consequences outlast the project. Before you sit through a single demo, run these checks first.
Highest-priority checks:
- Confirm data residency and whether your data leaves the UK
- Require a paid proof-of-concept (PoC) on your own production samples, not vendor-curated data
- Request SOC 2 Type II and ISO 27001 certificates under NDA
- Verify data export rights and deletion certification in writing
- Confirm SLA commitments at production throughput, not pilot scale
- Review exit and portability terms before any commercial discussion
The single most important step is a paid PoC on real data: vendors routinely optimise demos on curated inputs, and a controlled trial on 50–100 of your own production samples is the only way to separate genuine capability from a polished sales presentation. Gmdautomation, for example, supports structured PoC engagements for UK enterprise deployments, with security and compliance built into the process from the outset.
Table of Contents
- What categories does every AI vendor evaluation need to cover?
- What data controls and governance should you demand from AI vendors?
- How do you evaluate model choice, training data and bias risk?
- How should you design a PoC to avoid the demo trap?
- What integration and deployment questions should you ask?
- What pricing models and contract terms protect you at scale?
- What due diligence should you complete before signing?
- What are the red flags and green flags in AI vendor behaviour?
- How should IT teams organise the vendor evaluation process?
- A copyable checklist for IT and security teams
- How do you turn evaluation findings into a selection decision?
- Key takeaways
- The evaluation mistakes that cost organisations most
- Gmdautomation: enterprise AI deployment built for UK businesses
- Useful sources and further reading
What categories does every AI vendor evaluation need to cover?
A structured AI vendor selection process scores every candidate against the same dimensions. Without a fixed taxonomy, one vendor's slick demo skews the comparison and a fatal weakness in data handling gets buried under impressive accuracy numbers.
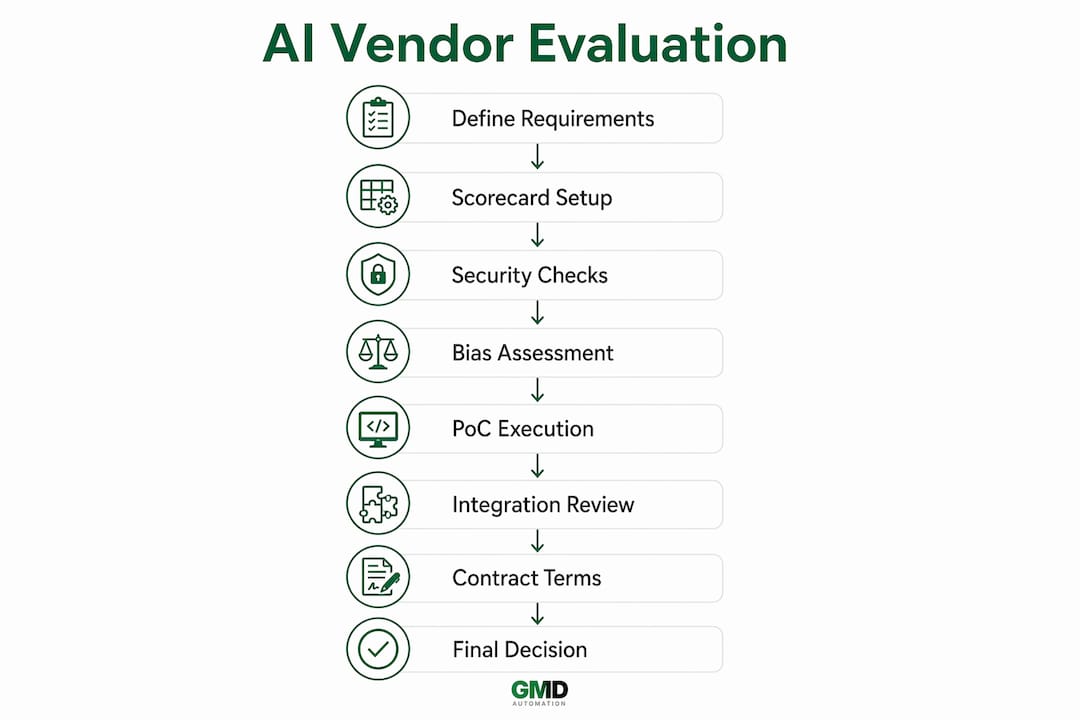
Weighted scoring across seven dimensions gives evaluations their backbone. The suggested starting weights are: business fit 25%, technical capability 25%, security and compliance 20%, commercial viability 20%, and long-term support 10%. Regulated UK sectors, including financial services, healthcare, and critical national infrastructure, should shift weight toward security and compliance, often to 30% or higher.
The seven core categories are:
-
Business fit: Does the tool solve your specific use case, not a generalised version of it?
-
Technical capability: Model quality, API reliability, latency, and throughput at your expected volume
-
Security and compliance: Certifications, data handling, UK GDPR posture, and audit artefacts
-
Data practices: Residency, encryption, training data use, opt-out options, and deletion rights
-
Integration and ops readiness: Native connectors, deployment model, MLOps maturity, and runbooks
-
Performance and validation: PoC results on your data, accuracy, false positive/negative rates
-
Commercial terms and exit: Pricing at scale, escalation caps, portability, and termination assistance
Pro Tip: Build a weighted scorecard in a spreadsheet before the first vendor call. Score every vendor on the same criteria with the same weights, then update scores after each interaction. This prevents a compelling demo from overriding a weak security posture — the single most common cause of regret in AI procurement.
Why businesses choose AI partners often comes down to fit and trust, but without a scorecard, "trust" is just another word for "impressive demo."
What data controls and governance should you demand from AI vendors?
Security teams need to translate UK GDPR obligations and internal governance requirements into specific vendor questions and contractual commitments before a PoC begins. Vague assurances at the sales stage become expensive disputes at renewal.
Data controls to verify:
- Data residency: confirm whether processing occurs within the UK or EEA, and whether any sub-processors are outside those regions
- Encryption in transit (TLS 1.2 minimum) and at rest (AES-256 or equivalent)
- Role-based access controls and audit logging for all data access events
- Whether customer data is used to retrain or fine-tune models, and whether an opt-out exists
- Data retention schedules and certified deletion on contract termination
- Incident notification timelines (UK GDPR requires notification to the ICO within 72 hours of awareness)
Contract clauses to insist on:
- A Data Processing Addendum (DPA) aligned to UK GDPR, naming all sub-processors
- Explicit prohibition on using your data for model training without written consent
- Certified data deletion within a defined period post-termination
- Data export in a documented, machine-readable format on request
- Defined incident response and notification obligations
Third-party audits sit at the top of the evidence hierarchy for security posture. SOC 2 Type II covers the controls that matter most for cloud-hosted AI services: availability, confidentiality, and security. ISO 27001 certification demonstrates a managed information security programme. Independent penetration test summaries, shared under NDA, show whether the vendor actually tests what they claim to protect. A vendor that holds only SOC 2 Type I, or refuses to share Type II under NDA, is a material concern for any production deployment.
For UK enterprises, the enterprise AI security architecture considerations go beyond certifications: they include how the vendor handles Subject Access Requests, whether the DPA covers automated decision-making under Article 22 UK GDPR, and what the vendor's lawful basis for processing actually is.
Pro Tip: Request SOC 2 Type II and penetration-test summaries under NDA before the technical PoC begins. If a vendor stalls or declines, that behaviour tells you more about their security culture than any certification ever could.
How do you evaluate model choice, training data and bias risk?
Understanding what sits under a vendor's product matters because the model choice, its training data, and the fine-tuning approach all carry risk that surfaces in production, not in demos.
At a high level, vendors fall into two categories. Platform or hyperscaler vendors (those building on foundation models from major AI providers) offer breadth and configurability, but require more in-house ML engineering to get production-ready. Specialised turnkey vendors deliver pre-built outcomes for a defined use case, which reduces internal engineering overhead but increases lock-in risk. The right choice depends on whether your organisation has the ML talent to manage a platform, or whether it needs a vendor to own the outcome end-to-end. This is the same build-vs-buy trade-off that shapes AI platform adoption decisions more broadly.
Questions to ask every vendor about their model:
- Which foundation model or models does the product use, and what is the versioning policy?
- Is customer data used to retrain or fine-tune the model? If so, can you opt out contractually?
- How are model updates communicated, and what is the rollback procedure if a new version degrades performance?
- What training data was used, and are there documented exclusions for sensitive categories?
Bias and fairness checks are not optional for any AI system touching decisions that affect people. Ask for sensitivity testing results across demographic groups relevant to your use case, documentation of concept-drift monitoring, and the vendor's process for identifying and remediating bias post-deployment.
Pro Tip: Prefer vendors that document model lineage and allow contractual opt-outs from training pipelines. A vendor that cannot explain what their model was trained on, or refuses to commit to opt-out rights in writing, is a significant risk signal — treat it as a near-disqualifier for regulated use cases.
Upskilling your team to interpret model documentation is also worth the investment. Understanding generative AI skills helps IT and security professionals ask sharper questions during vendor evaluations.
How should you design a PoC to avoid the demo trap?
The demo trap is the primary cause of failed AI projects. Vendors optimise demos on curated, clean data that bears little resemblance to your actual workflows. A well-scoped, paid PoC on your own production samples is the highest-signal evaluation step and should not be skipped. Budget guidance from vendor evaluation frameworks puts PoC costs at roughly €5,000–€20,000 depending on scope and vendor; the typical scope is 50–100 real samples, time-boxed to four weeks. Keep the scope narrow: one use case, one integration point, and a defined set of success criteria agreed in writing before the PoC begins.
Metrics to capture
| Metric | What to measure | Acceptable threshold (set before PoC) |
|---|---|---|
| Accuracy | Correct outputs / total samples | Agreed per use case |
| Latency | P95 response time under load | Per your SLA requirement |
| Throughput | Requests per second at peak | Match production peak volume |
| False positive rate | Incorrect positive classifications | Set per risk tolerance |
| False negative rate | Missed correct classifications | Set per risk tolerance |
| Confidence calibration | Alignment of confidence scores with actual accuracy | Vendor to provide |
| Human escalation rate | Proportion of outputs requiring human review | Baseline for cost modelling |
PoC meeting framework
- Kick-off (Day 1): Agree success criteria, sample selection methodology, and data handling protocol in writing
- Mid-point review (Day 10–14): Preliminary results, flag any data quality issues or scope creep
- Results readout (Day 28): Vendor presents results; your team independently validates on a held-out sample
- Kill/proceed decision (Day 30): Score against pre-agreed thresholds; no extensions without written justification
A PoC that does not meet pre-agreed thresholds is a kill signal, not a negotiation opener. Vendors who resist running PoCs on your data, or who push for extended pilots without defined success criteria, are telling you something important about how they will behave in production.
What integration and deployment questions should you ask?
Integration effort is consistently underestimated in AI vendor evaluations. The vendor's API may be excellent; the question is whether it fits your existing architecture without a six-month engineering project.
Integration checklist:
- Native connectors for your core systems (CRM, ERP, ITSM, data warehouse)
- REST API quality: versioning policy, rate limits, error handling, and developer documentation
- Webhook support for event-driven architectures
- Example runbooks for your deployment model (cloud, on-premises, or hybrid)
- Authentication and authorisation standards (OAuth 2.0, SAML, or equivalent)
Deployment model matters for UK data residency. Cloud deployments with UK or EEA data centres satisfy most UK GDPR requirements, but confirm sub-processor locations explicitly. On-premises deployments give maximum control but require the vendor to support air-gapped or private-cloud configurations. Hybrid models split processing between environments and need careful data-flow mapping to avoid inadvertent cross-border transfers.
MLOps readiness is a separate question from initial integration. Ask for the vendor's model versioning policy, their rollback procedure when a new model version degrades performance, their monitoring and alerting cadence, and their patching timeline for security vulnerabilities. A vendor with no documented rollback procedure is an operational risk from day one.
For teams assessing AI API integration options, the quality of developer documentation is often the best proxy for how much internal engineering time the integration will actually consume.
Pro Tip: During the PoC, run a simple data export test: extract your data in the vendor's stated export format and confirm you can import it into a neutral system. If the export fails or the format is undocumented, the vendor's exit claims are not credible.
What pricing models and contract terms protect you at scale?
Year-one total cost of ownership for an AI deployment typically runs 1.5–2x the headline monthly fee once integration engineering, ongoing tuning, customer success time, and human escalation costs are included. Model pricing can jump 2–5x from pilot to production in some vendor contracts. Model this before you sign, not after.
Common pricing shapes
- Subscription (flat monthly fee): Predictable but may include usage caps that trigger overages
- Consumption/usage-based: Scales with volume but creates cost uncertainty at peak; model at P95 volume, not average
- Seat plus overage: Fixed per-user fee with a variable component; confirm overage unit definition in writing
- Implementation fee plus recurring: Common for turnkey vendors; confirm what the implementation fee covers and whether it recurs
Contract terms to insist on
- Defined annual price escalation caps (CPI-linked or fixed percentage)
- Clear overage definitions with written notification thresholds before charges apply
- Termination assistance: the vendor must support data export and transition for a defined period post-termination
- Data export format, frequency, and schedule committed in the contract
- Performance SLAs at production throughput, with defined remedies for breach
For a simple production economics check, model three scenarios: current pilot volume, 3x pilot volume, and your expected peak. If the cost at 3x volume is not commercially viable, the pricing model is wrong for your use case regardless of how good the PoC results are. The enterprise AI ROI calculation only works if the production cost model is honest.
Pro Tip: Negotiate exit and portability terms before price. Once a vendor knows you are commercially committed, leverage disappears. Get data export format, termination assistance period, and model portability committed in the heads of terms, not as an afterthought in the final contract.
What due diligence should you complete before signing?
Due diligence on an AI vendor covers four areas: financial stability, security posture, legal standing, and customer references. Skipping any one of them is a risk that tends to surface at the worst possible moment.
Financial and organisational checks:
- Confirm the vendor's funding runway or profitability; a vendor with less than 12 months of runway is an operational risk for a multi-year deployment
- Check for executive continuity: high leadership turnover often precedes product or support degradation
- Search for active legal disputes, regulatory actions, or data breach disclosures
- Verify that the entity you are contracting with is the entity that holds the certifications
Security posture verification:
- SOC 2 Type II report: request the full report, not a summary; check the audit period and any exceptions noted
- ISO 27001 certificate: verify the scope and the certifying body
- Independent penetration test summary: confirm the test was conducted by a named third party within the last 12 months
- Vulnerability disclosure policy: does the vendor have a public policy and a defined response SLA?
- Incident history: ask directly whether the vendor has experienced a data breach or security incident in the last three years
Reference-check template:
Ask reference customers in your vertical these questions:
- What was the actual integration effort in engineering weeks, versus what the vendor quoted?
- How did accuracy and throughput hold up at production volume compared to the PoC?
- How responsive is support when something breaks at 2 AM?
- What did the contract cost at scale, and were there any pricing surprises?
- If you were starting again, would you choose the same vendor?
Vendor evidence hierarchy runs: peer-reviewed evidence, then major enterprise customer outcome data, then named customer case studies, then vendor case studies, then vendor marketing claims. Reference calls sit near the top of that hierarchy. Treat vendor-supplied case studies as a starting point for questions, not as evidence.
What are the red flags and green flags in AI vendor behaviour?
Vendor behaviour during the evaluation is a reliable predictor of vendor behaviour in production. A vendor that is evasive, slow, or defensive during a structured evaluation will be worse once you are commercially committed.
Red flags
- Refusal to run a paid PoC on your production data, or insistence on a demo-only evaluation
- Inability or unwillingness to provide SOC 2 Type II under NDA
- Evasive or inconsistent answers about whether customer data is used for model training
- No documented data export format or refusal to commit export rights in writing
- Pricing that is clear at pilot scale but vague or non-committal at production volume
- Resistance to signing a DPA before the PoC begins
- No named reference customers in your sector or integration context
Green flags
- Transparent pricing modelling at multiple volume scenarios, provided proactively
- Willingness to sign a DPA and, where applicable, a Business Associate Agreement before commercial commitment
- Documented model versioning, rollback procedures, and a clear patching cadence
- Named reference customers in your vertical who are reachable for calls
- Clear, written SLAs covering uptime, latency, and incident response at production throughput
- Proactive sharing of SOC 2 Type II and pen-test summaries without being asked twice
Pro Tip: Score vendor responsiveness during the evaluation itself: how quickly do they answer technical questions, how complete are their responses, and do they follow up without chasing? A vendor that takes two weeks to answer a security questionnaire during the sales process will not suddenly become responsive when you have a production incident.
How should IT teams organise the vendor evaluation process?
A properly structured enterprise AI vendor evaluation takes 8–12 weeks when done thoroughly. Evaluations compressed below eight weeks frequently miss security checks, reference calls, or legal review, and those gaps tend to surface as contract disputes or compliance failures.
Suggested timeline
| Week | Milestone | Owner |
|---|---|---|
| 1 | Define requirements, use case scope, and scoring criteria | IT lead, business sponsor |
| 2 | Issue RFP; initiate security review and DPA request | Procurement, security team |
| 3–4 | Vendor responses reviewed; shortlist to 2–3 vendors | IT lead, procurement |
| 4 | Paid PoC on production samples; reference calls in parallel | IT lead, security team |
| — | PoC results scored; reference call findings consolidated | IT lead, security team |
| — | Commercial negotiation; legal review of contract terms | Procurement, legal |
| 8–10 | Final security sign-off; contract execution | Security, legal, IT lead |
| 10–12 | Onboarding and integration planning | IT lead, vendor |
Roles and responsibilities (RACI)
| Activity | IT Lead | Security Team | Procurement | Legal | Business Sponsor |
|---|---|---|---|---|---|
| Define use case requirements | A | C | C | I | R |
| Issue and score RFP | R | C | A | I | C |
| PoC design and execution | A | C | I | I | R |
| Security posture review | C | A | I | I | I |
| Reference checks | R | C | C | I | C |
| Commercial negotiation | C | I | A | C | I |
| Contract review and sign-off | I | C | C | A | I |
| Final selection decision | C | C | C | I | A |
R = Responsible, A = Accountable, C = Consulted, I = Informed
Procurement, IT, and legal must be involved from the first pilot, not brought in at the contracting stage. Late involvement from legal or security creates friction, delays, and the kind of compliance failures that are expensive to remediate. The AI in procurement operations framework makes the case for cross-functional alignment from day one.
A copyable checklist for IT and security teams
Copy this into your procurement brief or vendor call notes. Tick each item before progressing a vendor to the next stage.
PoC and performance:
- Paid PoC agreed on 50–100 real production samples; budget guidance: €5,000–€20,000 depending on scope
- Success and kill criteria defined in writing before PoC begins
- Accuracy, latency, throughput, and escalation rate captured and scored
Security and compliance:
- SOC 2 Type II received and reviewed under NDA
- ISO 27001 certificate verified (scope and certifying body confirmed)
- Independent penetration test summary (within 12 months) received
- Vulnerability disclosure policy reviewed
Data and governance:
- Data residency confirmed (UK or EEA processing)
- DPA signed and aligned to UK GDPR
- Opt-out from model training confirmed in writing
- Data export format and schedule committed contractually
- Certified deletion on termination confirmed
Commercial and exit:
- Pricing modelled at pilot, 3x pilot, and peak production volume
- Annual escalation cap defined in contract
- Termination assistance period and data export committed
- SLAs confirmed at production throughput with defined remedies
Due diligence:
- Reference calls completed with customers in your vertical
- Financial stability confirmed (runway or profitability)
- Legal disputes and breach history checked
Gmdautomation supports UK enterprise deployments with security, compliance, and managed implementation built in, making it a practical partner option when working through this checklist.
How do you turn evaluation findings into a selection decision?
Scores and PoC results are inputs to a decision, not the decision itself. The final selection requires confidence across four dimensions: PoC evidence, legal and security sign-off, acceptable commercial terms, and a credible long-term support model.
Decision criteria:
- PoC results meet or exceed pre-agreed thresholds on accuracy, latency, and escalation rate
- Security team has signed off on the vendor's posture (SOC 2 Type II, ISO 27001, pen test)
- Legal has reviewed and approved the DPA, data export terms, and SLA commitments
- Commercial terms are viable at production volume, with escalation caps and exit rights confirmed
- At least two reference customers in your vertical have given positive assessments of support and real-world performance
If any of those five conditions is unmet, the vendor is not ready for a production commitment. A strong PoC result does not compensate for an unsigned DPA or a pricing model that becomes unviable at scale.
Negotiation priorities:
- Lock in exit rights and data portability before price negotiation begins
- Require performance SLAs at production throughput, not pilot conditions
- Confirm the termination assistance period covers at least 90 days of transition support
- Get pricing escalation caps in the heads of terms, not the final contract
Procurement handover to legal — clauses to include immediately:
- Data Processing Addendum (UK GDPR compliant, all sub-processors named)
- Data export format, frequency, and schedule
- Certified deletion within 30 days of termination
- Performance SLA with defined remedies (service credits or termination rights)
- Annual price escalation cap (CPI-linked or fixed)
- Termination assistance period and scope
Pro Tip: The AI SLA elements that matter most in production are not uptime percentages — they are latency at P95 load, incident response time, and the vendor's remediation commitment when accuracy degrades. Make sure those are in the contract, not just the sales deck.
Key takeaways
A paid PoC on your own production data, combined with verified security certifications and contractually committed exit rights, is the minimum standard for any UK enterprise AI vendor evaluation.
| Point | Details |
|---|---|
| PoC evidence is non-negotiable | Run a paid, time-boxed PoC on 50–100 real samples; budget guidance: €5,000–€20,000 depending on scope. Pre-agree kill criteria before it begins. |
| Model production costs, not pilot pricing | Year-one TCO typically runs 1.5–2x the headline fee; model at 3x pilot volume before signing. |
| Data controls must be contractual | Require a UK GDPR-aligned DPA, opt-out from model training, and certified deletion in writing. |
| Cross-functional governance from day one | Procurement, IT, legal, and security must be involved from the first pilot, not at contracting. |
| Gmdautomation as a UK deployment partner | Gmdautomation offers enterprise-grade AI deployments with managed implementation and compliance support for UK businesses. |
The evaluation mistakes that cost organisations most
The most expensive AI procurement mistakes share a common structure: teams move fast on the parts that feel good (demos, capability discussions, pricing headlines) and slow on the parts that are uncomfortable (legal review, security questionnaires, exit terms). By the time the discomfort surfaces, the organisation is commercially committed.
The demo trap deserves more attention than it typically gets. A vendor that refuses to run a PoC on your production data is not being difficult; they are protecting their conversion rate. Real data exposes edge cases, failure modes, and accuracy gaps that a curated demo never will. The cost of skipping a paid PoC is not the PoC fee; it is the cost of a failed deployment, a renegotiation from a position of weakness, or a data incident that could have been caught in a four-week trial.
Engaging legal late is the other failure mode that comes up repeatedly. A DPA that is not signed before the PoC begins means your production data may have been processed under terms you never agreed to. Pricing escalation clauses buried in a 60-page MSA are not a legal team problem; they are a procurement problem that legal gets handed too late to fix. The fix is structural: legal and security review the vendor's standard contract terms before the PoC, not after the business sponsor has already decided they want this vendor.
One more thing that rarely gets said plainly: the evaluation process itself is a negotiation. Vendors know that once you have invested six weeks in a PoC and reference calls, your switching cost has risen. The time to negotiate exit rights, portability, and SLAs is before you are emotionally and commercially invested, not after. Teams that treat the evaluation as purely technical and leave commercial terms to the end consistently get worse contracts than teams that run both tracks in parallel.
Gmdautomation: enterprise AI deployment built for UK businesses
UK enterprises that have completed a rigorous vendor evaluation often arrive at the same conclusion: the hardest part is not finding a capable AI system, it is finding one that is genuinely ready for production, compliant with UK data requirements, and supported by a team that stays engaged after go-live.
Gmdautomation is built specifically for that gap. The offering covers enterprise-grade AI automation with managed implementation, ongoing operation, maintenance, and optimisation, all under a predictable monthly subscription with no upfront capital cost. Security and UK GDPR compliance are built into the deployment architecture, not bolted on as an afterthought. Gmdautomation supports AI automation for UK businesses across sectors, with flexible scaling and a transparent pricing model that holds at production volume.
For IT and security teams that have just worked through the evaluation framework above, the practical next step is straightforward: request a structured demo on your use case, and ask Gmdautomation to walk through their security posture, data residency controls, and SLA commitments against your checklist. That conversation is available now at gmdautomation.ai.
Useful sources and further reading
The sources below are worth consulting directly for governance, compliance, and procurement guidance relevant to UK enterprise AI adoption.
- ICO (Information Commissioner's Office): The UK's primary authority on data protection and UK GDPR. The ICO's guidance on AI and automated decision-making is the starting point for any DPA or Article 22 assessment. ico.org.uk
- NIST AI Risk Management Framework: The NIST framework provides a structured approach to AI risk identification, measurement, and management, widely referenced in UK enterprise governance programmes.
- Gartner AI vendor evaluation research: Gartner's published research on AI vendor selection covers market positioning, capability assessment, and procurement considerations for enterprise buyers.
- Safe AI Australia governance templates: The AI vendor evaluation checklist from Safe AI Australia provides a practical governance template that translates well to UK enterprise contexts.
- Kurums five-axis selection framework: A structured AI vendor selection guide covering fit, data handling, pricing, reliability, and exit terms, with practical scoring guidance.
- AI and automation in practice: For context on incremental AI value and staged adoption, the partner article on AI and automation transforming businesses covers operational adoption patterns relevant to PoC scoping.
- Gmdautomation resources: The Gmdautomation blog covers enterprise AI security architecture, SLA design, API integration, and ROI modelling for UK deployments.